Handling Parameters in Authorization Requests and Token Requests
How to manage parameters in authorization and token requests through Authlete APIs.
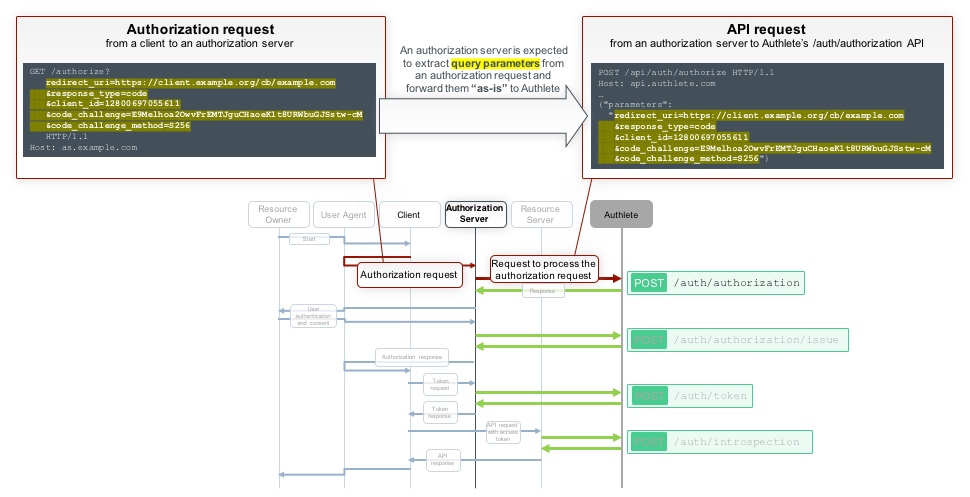
Using “parameters” on /auth/authorization APIAn authorization server frontend is expected to pass parameters, which are received at authorization endpoints and token endpoints, to respective Authlete APIs as-is, i.e. you usually MUST NOT modify/pre-process them.For example, if you want to check values of scope parameter in an authorization request, you don’t have to have the authorization server to check them before invoking Authlete’s /auth/authorization API; the server should include whole query parameters as a value of parameters key of the API. Authlete will be making a response that includes values, that are verified by Authlete, in scope parameter. Then your authorization server frontend will be able to check those verified scope values.There are some risks to implement your own verification/modification processes before invoking /auth/authorization or /auth/token API; You might fail to use Authlete’s functions for OAuth / OpenID Connect, such as protocol handling and error checking. In the worst-case scenario, your authorization server would be non-compliant to OAuth / OpenID Connect if you don’t fully understand such standards.
{"docsConfig":{"theme":"mint","$schema":"https://mintlify.com/docs.json","name":"Authlete Documentation","colors":{"primary":"#0057B7","light":"#4D8FEA","dark":"#0057B7"},"logo":{"light":"https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/authlete-blue-horizontal-logo.svg?fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=ed123a3de8b7791dffde03e7705c7460","dark":"https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/authlete-blue-horizontal-logo.svg?fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=ed123a3de8b7791dffde03e7705c7460"},"favicon":{"light":"https://mintcdn.com/authlete/gV1fxQkuH3uz_H3j/images/favicon-32x32.png?fit=max\u0026auto=format\u0026n=gV1fxQkuH3uz_H3j\u0026q=85\u0026s=9838a40b23e11ab35d7737e4c94a2d9a","dark":"https://mintcdn.com/authlete/gV1fxQkuH3uz_H3j/images/favicon-32x32.png?fit=max\u0026auto=format\u0026n=gV1fxQkuH3uz_H3j\u0026q=85\u0026s=9838a40b23e11ab35d7737e4c94a2d9a"},"api":{"openapi":"https://spec.speakeasy.com/authlete/sdk-workspace/authlete-api-explorer-with-code-samples","playground":{"display":"interactive","proxy":true},"examples":{"languages":["typescript","ruby","go","shell"],"autogenerate":true},"mdx":{"auth":{"method":"bearer"},"server":"https://us.authlete.com"}},"navbar":{"primary":{"type":"button","label":"Get Started","href":"https://console.authlete.com/"}},"footer":{"socials":{"x":"https://x.com/authlete","github":"https://github.com/authlete","linkedin":"https://linkedin.com/company/authlete"}},"contextual":{"options":["copy","view","chatgpt","claude","mcp","cursor"],"display":"header"},"thumbnails":{"fonts":{"family":"Noto Sans JP"}},"markdown":{"instructions":["### Authlete versions","Authlete 3.0 is the current version. Unless the user says they use another version, answer for Authlete 3.0 using the 3.x documentation.","Documentation for Authlete 2.x (pages under `/v2/` and `/ja/v2/`) is for the legacy version. Refer to it only when the user is on Authlete 2.x.","","### Authlete architecture","Authlete is a backend engine for OAuth 2.0 and OpenID Connect processing. End users and client applications do not call it directly; the service provider's authorization server and API server call Authlete's APIs. Authlete handles protocol processing and token, client, and service management, while the service provider owns the OAuth/OIDC endpoints and user authentication.","See [Architecture](https://developers.authlete.com/get-started/introduction-to-authlete/architecture.md).","","### Concepts","If the user is new to Authlete, read these pages first:","- [Request and Response](https://developers.authlete.com/get-started/concepts/request-and-response.md): Core API requests pass the client's request parameters as-is, and responses return `resultCode`, `action`, and `responseContent`.","- [Action Handling](https://developers.authlete.com/get-started/concepts/action-handling.md): Branch on `action`, never on `resultCode`, and map each action to the HTTP response your server returns.","- [Two-Step API Calls](https://developers.authlete.com/get-started/concepts/two-step-api-calls.md): Actions such as `INTERACTION` are completed with a second call (`/auth/authorization/issue` or `/auth/authorization/fail`) linked by a `ticket`.","- [Management API Overview](https://developers.authlete.com/get-started/concepts/overview.md): The Management API configures services, manages clients, and operates issued tokens, separately from the protocol flows handled by the Core API.","- [API Authentication](https://developers.authlete.com/get-started/concepts/authentication.md): Authlete APIs use bearer tokens: a Service Access Token (one service) or an Organization Token (the whole organization)."]},"styling":{"latex":false},"navigation":{"languages":[{"language":"en","default":true,"href":"get-started/introduction-to-authlete"},{"language":"ja","href":"ja/get-started/introduction-to-authlete"}]}},"deployment":{"deploymentMetadataValue":{"subdomain":"authlete","hasAudioNarration":false,"actualSubdomain":"authlete","customDomains":["developers.authlete.com"],"gitSource":{"type":"github","owner":"authlete","repo":"developer-docs","deployBranch":"main","contentDirectory":"","isPrivate":true,"mountPath":"","label":""},"chroma":{"liveDeploymentHistoryId":"6ad86bfbbcc1b0bac5b9a633","collectionId":"102eb795-336b-4b91-aae6-f3939575b917","schemaVersion":"v3","latestBuiltDeploymentHistoryId":"6ad86bfbbcc1b0bac5b9a633"},"feedback":{"thumbs":true,"agentFeedback":true},"entitlements":{"AI_CHAT":{"status":"DISABLED"}},"buildId":"6ad86bfbbcc1b0bac5b9a633","clientVersion":"0.0.3965","searchFilterCounts":[{"language":"en","tag":"Release Notes","count":103},{"language":"ja","tag":"リリースノート","count":103},{"language":"ja","tag":"設定リファレンス","count":92},{"language":"default","tag":"API Reference","count":87},{"language":"default","tag":"Authlete","count":87},{"language":"en","tag":"Configuration Reference","count":83},{"language":"en","tag":"Protocols \u0026 Flows","count":46},{"language":"en","tag":"Deployment \u0026 Operations","count":44},{"language":"ja","tag":"プロトコル \u0026 フロー","count":42},{"language":"ja","tag":"デプロイと運用","count":39},{"language":"ja","tag":"トークン \u0026 クレーム","count":38},{"language":"ja","tag":"はじめに","count":34},{"language":"ja","tag":"エンドポイント","count":33},{"language":"en","tag":"Get Started","count":32},{"language":"en","tag":"Tokens and Claims","count":28},{"language":"default","tag":"Client Management","count":26},{"language":"en","tag":"Endpoints","count":25},{"language":"en","tag":"Server Releases (v2.2)","count":23},{"language":"en","tag":"Server Releases (v2.3)","count":23},{"language":"ja","tag":"サーバーリリース (v2.2)","count":23},{"language":"ja","tag":"サーバーリリース (v2.3)","count":23},{"language":"en","tag":"Server Releases (v3.0)","count":20},{"language":"ja","tag":"サーバーリリース (v3.0)","count":20},{"language":"default","tag":"Verifiable Credential Issuer","count":11},{"language":"default","tag":"Service Management","count":6},{"language":"default","tag":"Authorization Endpoint","count":5},{"language":"default","tag":"Token Operations","count":5},{"language":"default","tag":"CIBA","count":4},{"language":"default","tag":"Dynamic Client Registration","count":4},{"language":"default","tag":"Hardware Security Key","count":4}],"searchSettings":{"maxResults":7}},"assistantConfig":{},"hasChatPermissions":false,"hasWebMcpPermissions":false,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-v7-file-tree","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"pause-universal-search-reconcile","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"per-site-search-delta","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-private-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-nav-generations","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"byok-sep-25","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"vite-origin","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-agent-model-picker","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-updated-9-15","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"privacy":{"consentBanner":{"enabled":true}},"isAtlas":false,"googleFontsInlined":false},"customCss":[{"filePath":"style.css","content":"#content-area,#navbar,#sidebar,[data-sidebar],body{background-image:none!important}.dynamic-curl-wrapper{width:100%;max-width:100%;min-width:0}.dynamic-curl-output{width:100%!important;max-width:100%!important;min-width:0!important}table[style*=tableLayout] td:last-child{overflow:hidden;min-width:0}table[style*=tableLayout] input{min-width:0}"}],"page":{"pagePath":"configuration-reference/endpoints/handling-request-parameters","slug":"/configuration-reference/endpoints/handling-request-parameters","pageMetadata":{"title":"Handling Parameters in Authorization Requests and Token Requests","description":"How to manage parameters in authorization and token requests through Authlete APIs.","sidebarTitle":"Handling Parameters in Client Requests","href":"/configuration-reference/endpoints/handling-request-parameters"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"How to manage parameters in authorization and token requests through Authlete APIs.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,em:`em`,p:`p`,strong:`strong`,..._provideComponents(),...props.components},{OptimizedImage}=_components;if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);return _jsxs(_Fragment,{children:[_jsx(OptimizedImage,{src:`https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/configuration-reference/endpoints/request-parameters.png?fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=bb7b99c8b22fa1a6e28026e576537bc0`,alt:`request-parameters`,\"data-og-width\":`970`,width:`970`,\"data-og-height\":`497`,height:`497`,\"data-path\":`configuration-reference/endpoints/request-parameters.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/configuration-reference/endpoints/request-parameters.png?w=280\u0026fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=cc9282f6e6541a9837eae63bac6ae775 280w, https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/configuration-reference/endpoints/request-parameters.png?w=560\u0026fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=69ecf7f5ae80c41553d772eecb4f989c 560w, https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/configuration-reference/endpoints/request-parameters.png?w=840\u0026fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=9d0d8c7bfaa5fbcaaab1113e7bc8bd6a 840w, https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/configuration-reference/endpoints/request-parameters.png?w=1100\u0026fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=2323fe7192a97edd0562f859b349d718 1100w, https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/configuration-reference/endpoints/request-parameters.png?w=1650\u0026fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=26b3dd3a2aa9e833bacff75f128f61e1 1650w, https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/configuration-reference/endpoints/request-parameters.png?w=2500\u0026fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=a41187babe8f5942fb3fc48cb0a42426 2500w`}),`\n`,_jsx(_components.p,{children:_jsx(_components.em,{children:`Using “parameters” on /auth/authorization API`})}),`\n`,_jsxs(_components.p,{children:[`An authorization server frontend is expected to pass parameters, which are received at authorization endpoints and token endpoints, to respective Authlete APIs `,_jsx(_components.strong,{children:`as-is, i.e. you usually MUST NOT modify/pre-process them`}),`.`]}),`\n`,_jsxs(_components.p,{children:[`For example, if you want to check values of scope parameter in an authorization request, you don’t have to have the authorization server to check them before invoking Authlete’s `,_jsx(_components.a,{href:`/api-reference/authorization-endpoint/process-authorization-request`,children:`/auth/authorization`}),` API; the server should include whole query parameters as a value of parameters key of the API. Authlete will be making a response that includes values, that are verified by Authlete, in scope parameter. Then your authorization server frontend will be able to check those verified scope values.`]}),`\n`,_jsxs(_components.p,{children:[`There are some risks to implement your own verification/modification processes before invoking `,_jsx(_components.a,{href:`/api-reference/authorization-endpoint/process-authorization-request`,children:`/auth/authorization`}),` or `,_jsx(_components.a,{href:`/api-reference/token-endpoint/process-token-request`,children:`/auth/token`}),` API; You might fail to use Authlete’s functions\\xA0 for OAuth / OpenID Connect, such as protocol handling and error checking. In the worst-case scenario, your authorization server would be non-compliant to OAuth / OpenID Connect if you don’t fully understand such standards.`]})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"config":{},"pageMetadata":{"title":"Handling Parameters in Authorization Requests and Token Requests","description":"How to manage parameters in authorization and token requests through Authlete APIs.","sidebarTitle":"Handling Parameters in Client Requests","href":"/configuration-reference/endpoints/handling-request-parameters"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[],"codeExamples":{}},"jsLinks":["/_mintlify/custom/authlete/a07b398e9c8556ba/snippets/oauth-dynamic.js"],"subdomain":"authlete","siteName":"Authlete Documentation","title":"Handling Parameters in Authorization Requests and Token Requests - Authlete Documentation","navMaps":{"firstHrefInVersion":{"3.x":{"href":"/configuration-reference/endpoints/handling-request-parameters","matchLevel":0},"2.x":{"href":"/ja/configuration-reference/endpoints/handling-request-parameters","matchLevel":1}},"firstHrefInLanguage":{"en":{"href":"/configuration-reference/endpoints/handling-request-parameters","matchLevel":0},"ja":{"href":"/ja/configuration-reference/endpoints/handling-request-parameters","matchLevel":1}}},"lastModified":"2026-07-13T19:59:23.560Z","originalFileLocation":"configuration-reference/endpoints/handling-request-parameters.mdx","locale":"en"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"system\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"How to manage parameters in authorization and token requests through Authlete APIs.\">\u003cmeta data-mint-head name=\"application-name\" content=\"Authlete Documentation\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"Handling Parameters in Authorization Requests and Token Requests - Authlete Documentation\">\u003cmeta data-mint-head property=\"og:description\" content=\"How to manage parameters in authorization and token requests through Authlete APIs.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"Authlete Documentation\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://authlete.mintlify.app/_mintlify/api/og/v2?division=Overview\u0026amp;title=Handling+Parameters+in+Authorization+Requests+and+Token+Requests\u0026amp;description=How+to+manage+parameters+in+authorization+and+token+requests+through+Authlete+APIs.\u0026amp;theme=9a33e57959880538f1449aa0\u0026amp;signature=b68820c0c3133a96d7ceae3df377b88994fea4735854da823e5cf0881c9c8f53\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"Handling Parameters in Authorization Requests and Token Requests - Authlete Documentation\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"How to manage parameters in authorization and token requests through Authlete APIs.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://authlete.mintlify.app/_mintlify/api/og/v2?division=Overview\u0026amp;title=Handling+Parameters+in+Authorization+Requests+and+Token+Requests\u0026amp;description=How+to+manage+parameters+in+authorization+and+token+requests+through+Authlete+APIs.\u0026amp;theme=9a33e57959880538f1449aa0\u0026amp;signature=b68820c0c3133a96d7ceae3df377b88994fea4735854da823e5cf0881c9c8f53\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/mintlify-assets/_mintlify/favicons/authlete/aQ4BxffFlrUzvna2/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"Authlete Documentation\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#0057B7\">\u003clink data-mint-head rel=\"canonical\" href=\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/configuration-reference/endpoints/handling-request-parameters.md\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"en\" href=\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"ja\" href=\"https://developers.authlete.com/ja/configuration-reference/endpoints/handling-request-parameters\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"x-default\" href=\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://developers.authlete.com/#organization\",\"name\":\"Authlete Documentation\",\"url\":\"https://developers.authlete.com\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/authlete/EJDZNZMvOu_9CJHJ/authlete-blue-horizontal-logo.svg?fit=max\u0026auto=format\u0026n=EJDZNZMvOu_9CJHJ\u0026q=85\u0026s=ed123a3de8b7791dffde03e7705c7460\"}},{\"@type\":\"WebSite\",\"@id\":\"https://developers.authlete.com#website\",\"name\":\"Authlete Documentation\",\"url\":\"https://developers.authlete.com\",\"publisher\":{\"@id\":\"https://developers.authlete.com/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters#webpage\",\"url\":\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters\",\"name\":\"Handling Parameters in Authorization Requests and Token Requests\",\"description\":\"How to manage parameters in authorization and token requests through Authlete APIs.\",\"dateModified\":\"2026-07-13T19:59:23.560Z\",\"isPartOf\":{\"@id\":\"https://developers.authlete.com#website\"},\"breadcrumb\":{\"@id\":\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Authlete Documentation\",\"item\":\"https://developers.authlete.com\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Handling Parameters in Authorization Requests and Token Requests\",\"item\":\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters#article\",\"headline\":\"Handling Parameters in Authorization Requests and Token Requests\",\"name\":\"Handling Parameters in Authorization Requests and Token Requests\",\"description\":\"How to manage parameters in authorization and token requests through Authlete APIs.\",\"url\":\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters\",\"mainEntityOfPage\":{\"@id\":\"https://developers.authlete.com/configuration-reference/endpoints/handling-request-parameters#webpage\"},\"dateModified\":\"2026-07-13T19:59:23.560Z\",\"publisher\":{\"@id\":\"https://developers.authlete.com/#organization\"},\"isPartOf\":{\"@id\":\"https://developers.authlete.com#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"Authlete Documentation\",\"creator\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","siteName":"Authlete Documentation","nav":{"global":null,"languages":[{"language":"en","default":true,"versions":[{"version":"3.x","default":true,"tabs":[{"tab":"Get Started","pages":[{"title":"Get Started","href":"/get-started/introduction-to-authlete/overview"}]},{"tab":"API Reference","pages":[{"title":"API Reference","href":"/api-reference/service-management/get-service"}]},{"tab":"Protocols \u0026 Flows","pages":[{"title":"Protocols \u0026 Flows","href":"/protocols-and-flows/basic-oauth-oidc-flows/oauth-2-0-and-openid-connect-authorization-endpoints"}]},{"tab":"Configuration Reference","groups":[{"group":"Endpoints","pages":[{"group":"Overview","pages":[{"title":"Handling Parameters in Authorization Requests and Token Requests","sidebarTitle":"Handling Parameters in Client Requests","href":"/configuration-reference/endpoints/handling-request-parameters"},{"title":"Handling Responses from Authlete API","description":"Handling responses from Authlete API and the importance of processing based on the action parameter rather than the resultCode value.","sidebarTitle":"Handling Responses from Authlete API","href":"/configuration-reference/endpoints/handling-responses-from-authlete-apis"}]},{"group":"Authorization EP","pages":[{"title":"Implementing an Authorization Endpoint with Authlete","sidebarTitle":"Implementing AuthZ EP","href":"/configuration-reference/endpoints/implementing-an-authorization-endpoint-with-authlete"},{"title":"Ticket Parameter in Authorization Endpoint","sidebarTitle":"Handling Ticket Parameter","href":"/configuration-reference/endpoints/ticket-parameter-in-authorization-endpoint"},{"title":"There Is No Entity Having the Ticket Error","href":"/configuration-reference/endpoints/when-seeing-the-error-of-there-is-no-entity-having-the-ticket-specified"},{"title":"Required Scope When response_type Contains id_token","sidebarTitle":"Required Scope for id_token","href":"/configuration-reference/endpoints/when-a-response-type-parameter-contains-id-token"},{"title":"Requiring clients to use PKCE for their authorization requests","sidebarTitle":"Enforcing PKCE","href":"/configuration-reference/endpoints/requiring-clients-to-use-pkce-for-their-authorization-requests"},{"title":"Requiring clients to specify S256 when using PKCE for their authorization requests","sidebarTitle":"Enforcing S256 (PKCE)","href":"/configuration-reference/endpoints/requiring-clients-to-specify-s256-when-using-pkce"},{"title":"Using Request Object","href":"/configuration-reference/endpoints/using-request-objects"},{"title":"JWT Secured Authorization Requests (JAR)","sidebarTitle":"Configuring JAR","href":"/configuration-reference/endpoints/jwt-secured-authorization-requests-jar"},{"title":"Configuring JARM","sidebarTitle":"Configuring JARM","href":"/configuration-reference/endpoints/enabling-jarm"}]},{"group":"Token EP","pages":[{"title":"Configuring Client Authentication","sidebarTitle":"Configuring Client AuthN","href":"/configuration-reference/endpoints/configuring-client-authentication"},{"title":"Client authentication using client_secret_jwt method","sidebarTitle":"client_secret_jwt","href":"/configuration-reference/endpoints/client-authentication-using-client-secret-jwt-method"},{"title":"Client authentication using private_key_jwt method","sidebarTitle":"private_key_jwt","href":"/configuration-reference/endpoints/client-authentication-using-private-key-jwt-method"},{"title":"Client authentication using tls_client_auth method","sidebarTitle":"tls_client_auth","href":"/configuration-reference/endpoints/client-authentication-using-tls-client-auth-method"},{"title":"Strict checking on client authentication parameters","sidebarTitle":"Strict Parameter Checking","href":"/configuration-reference/endpoints/strict-checking-on-client-authentication-parameters"}]},{"group":"Introspection EP","pages":[{"title":"Protected Resource","sidebarTitle":"Implementing the Introspection Endpoint","href":"/configuration-reference/endpoints/protected-resource"},{"title":"Use cases for two introspection APIs","sidebarTitle":"Two Introspection APIs","href":"/configuration-reference/endpoints/use-cases-for-two-introspection-apis"},{"title":"Introspection Response for Expired Access Token","sidebarTitle":"Introspection on Expired Token","href":"/configuration-reference/endpoints/introspection-response-for-expired-access-token"},{"title":"responseContent of a Valid Introspection Response","sidebarTitle":"responseContent on Success","href":"/configuration-reference/endpoints/responsecontent-of-a-valid-introspection-response"},{"title":"Checking if an access token has particular scopes","sidebarTitle":"Checking Scopes for Token","href":"/configuration-reference/endpoints/checking-if-an-access-token-has-particular-scopes"},{"title":"JWT Response for OAuth Token Introspection","sidebarTitle":"JWT Introspection Response","href":"/configuration-reference/endpoints/jwt-response-for-oauth-token-introspection"}]},{"group":"UserInfo EP","pages":[{"title":"Adding Custom Claims to Userinfo API Responses","href":"/configuration-reference/endpoints/adding-custom-claims-to-userinfo-api-responses"},{"title":"Access Token Verification in Userinfo API","href":"/configuration-reference/endpoints/access-token-verification-in-userinfo-api"}]},{"group":"PAR EP","pages":[{"title":"Pushed Authorization Requests (PAR)","sidebarTitle":"Configuring PAR","href":"/configuration-reference/endpoints/pushed-authorization-requests-par"}]},{"group":"Device AuthZ EP","pages":[{"title":"Device Flow (OAuth 2.0 Device Authorization Grant)","sidebarTitle":"Configuring Device Flow","href":"/v2/configuration-reference/endpoints/enabling-device-flow"}]}]},{"group":"Tokens and Claims","pages":[{"group":"Lifecycle \u0026 Policies","pages":[{"title":"How Authlete Determines Token Duration","sidebarTitle":"Token Duration Policy","href":"/configuration-reference/tokens-and-claims/how-authlete-determines-token-duration"},{"title":"Token Duration Per Scope","href":"/configuration-reference/tokens-and-claims/token-duration-per-scope"},{"title":"Token Duration Per Client","href":"/configuration-reference/tokens-and-claims/token-duration-per-client"},{"title":"Changing Token Duration","href":"/configuration-reference/tokens-and-claims/changing-token-duration"},{"title":"Managing Authorizations (Issued Tokens) Granted for Client by User","sidebarTitle":"Managing User-Granted Tokens","href":"/configuration-reference/tokens-and-claims/managing-authorizations-issued-tokens-granted-for-a-client-by-a-user"},{"title":"Updating Issued Token(s)","href":"/configuration-reference/tokens-and-claims/updating-issued-token-s"},{"title":"Token Revocation Policy","href":"/configuration-reference/tokens-and-claims/token-revocation-policy"},{"title":"Authlete's Policy on Sweeping Unused Tokens","sidebarTitle":"Token Sweeping Policy","href":"/configuration-reference/tokens-and-claims/authletes-policy-on-sweeping-unused-tokens"}]},{"group":"Access Token","pages":[{"title":"Using JWT-Based Access Tokens","sidebarTitle":"Using JWT Access Tokens","href":"/configuration-reference/tokens-and-claims/using-jwt-based-access-tokens"},{"title":"Adding Extra Properties to Access Token","sidebarTitle":"Access Token Properties","href":"/configuration-reference/tokens-and-claims/how-to-add-extra-properties-to-an-access-token"},{"title":"Enabling Single Access Token","href":"/configuration-reference/tokens-and-claims/enabling-single-access-token-per-subject"},{"title":"Getting a List of Issued Access Tokens","sidebarTitle":"Listing Issued Access Tokens","href":"/configuration-reference/tokens-and-claims/getting-a-list-of-issued-access-tokens"},{"title":"Issuing Two Access Tokens Through Hybrid Flow","sidebarTitle":"Access Tokens in Hybrid Flow","href":"/configuration-reference/tokens-and-claims/issuing-two-access-tokens-through-hybrid-flow"}]},{"group":"Refresh Token","pages":[{"title":"Refresh tokens after being used","href":"/configuration-reference/tokens-and-claims/refresh-tokens-after-being-used"},{"title":"Enabling Refresh Token Issuance","href":"/configuration-reference/tokens-and-claims/how-to-enable-issuing-of-a-refresh-token"}]},{"group":"ID Token","pages":[{"title":"Identifying Claims Expected to Be Included in ID Token","sidebarTitle":"Identifying Claims","href":"/configuration-reference/tokens-and-claims/identifying-claims-expected-to-be-included-into-an-id-token"},{"title":"Adding Claims to ID Token","sidebarTitle":"Adding Claims","href":"/configuration-reference/tokens-and-claims/adding-claims-to-an-id-token"},{"title":"Custom Header Claims in ID Tokens","sidebarTitle":"Custom Header Claims","href":"/configuration-reference/tokens-and-claims/custom-header-claims-in-id-tokens"},{"title":"Changing Signing Key for ID Tokens","sidebarTitle":"Changing Signing Key","href":"/configuration-reference/tokens-and-claims/changing-signing-key-for-id-tokens"},{"title":"Generating Encrypted ID Tokens","sidebarTitle":"Generating Encrypted ID Tokens","href":"/configuration-reference/tokens-and-claims/generating-encrypted-id-tokens"}]},{"group":"PoP (Proof-of-Possession) Token","pages":[{"title":"Issuing mutual-TLS certificate-bound access tokens","sidebarTitle":"mTLS Certificate Binding","href":"/configuration-reference/tokens-and-claims/issuing-mutual-tls-certificate-bound-access-tokens"},{"title":"Using DPoP","sidebarTitle":"DPoP","href":"/configuration-reference/tokens-and-claims/using-dpop"}]},{"group":"Scope","pages":[{"title":"Scope Attributes","href":"/configuration-reference/tokens-and-claims/scope-attributes"},{"title":"Using “Parameterized Scopes”","sidebarTitle":"Parameterized Scopes","href":"/configuration-reference/tokens-and-claims/using-parameterized-scopes"},{"title":"Registering Localized Descriptions for Custom Scopes","sidebarTitle":"Localized Scope Descriptions","href":"/configuration-reference/tokens-and-claims/registering-localized-descriptions-for-custom-scopes"},{"title":"Letting Resource Owners Choose Scopes to Be Authorized","sidebarTitle":"Authorizing Scopes by User","href":"/configuration-reference/tokens-and-claims/letting-resource-owners-choose-scopes-to-be-authorized"}]},{"group":"RAR","pages":[{"title":"Rich Authorization Requests (RAR)","sidebarTitle":"Configuring RAR","href":"/configuration-reference/tokens-and-claims/rich-authorization-requests-rar"}]},{"group":"Resource Indicators","pages":[{"title":"Resource Indicators","sidebarTitle":"Using Resource Indicators","href":"/configuration-reference/tokens-and-claims/resource-indicators"}]}]},{"group":"Key Management","pages":[{"title":"JWK Set Settings for Authlete Service","sidebarTitle":"JWK Set for Service","href":"/configuration-reference/key-management/jwk-set-settings-for-an-authlete-service"},{"title":"JWK Set Settings for OAuth / OIDC client","sidebarTitle":"JWK Set for Client","href":"/configuration-reference/key-management/jwk-set-settings-for-an-oauth-oidc-client"}]},{"group":"Metadata","pages":[{"title":"Publishing OpenID Provider Metadata and OAuth 2.0 Authorization Server Metadata","sidebarTitle":"Publishing Server Metadata","href":"/configuration-reference/metadata/publishing-metadata"},{"title":"Publishing JWK Set","href":"/configuration-reference/metadata/publishing-a-jwk-set"}]},{"group":"Error Handling \u0026 Debugging","pages":[{"title":"Interpreting Authlete's Result Codes","sidebarTitle":"Authlete's Result Codes","href":"/configuration-reference/error-handling-debugging/interpreting-authletes-result-codes"},{"title":"Suppressing Error Details in responseContent","sidebarTitle":"Suppressing Error Details","href":"/configuration-reference/error-handling-debugging/suppressing-error-details-in-responsecontent"},{"title":"Generating Error Response Using Fail API","sidebarTitle":"Generating Error Response","href":"/configuration-reference/error-handling-debugging/generating-error-response-using-fail-api"},{"title":"Service Flags","sidebarTitle":"Service Flags","href":"/configuration-reference/error-handling-debugging/flags-supported-in-authlete"}]},{"group":"Security","pages":[{"title":"How to Provide User Attributes","sidebarTitle":"Managing User Attributes","href":"/configuration-reference/security/how-to-provide-user-attributes"},{"title":"Audit Logs","href":"/configuration-reference/security/audit-logs"}]},{"group":"Client Management","pages":[{"title":"Client Attributes","href":"/configuration-reference/client-management/client-attributes"},{"title":"Client Authorized by User","href":"/configuration-reference/client-management/authletes-policy-on-managing-clients-which-have-been-authorized-by-user"},{"title":"Token Revocation upon Client Deletion","sidebarTitle":"Token Revocation upon Client Deletion","href":"/configuration-reference/client-management/token-management-policy-when-deleting-clients"}]},{"group":"Service Settings","pages":[{"title":"Creating an OAuth/OpenID Connect Service","href":"/configuration-reference/service-settings/creating-an-oauth-openid-connect-service"},{"title":"Service Configurations","sidebarTitle":"All Service Settings","href":"/configuration-reference/service-settings/service-management"}]}]},{"tab":"Deployment \u0026 Operations","pages":[{"title":"Deployment \u0026 Operations","href":"/deployment-and-operations/terraform/introduction"}]},{"tab":"Release Notes","pages":[{"title":"Release Notes","href":"/release-notes/console/2026-09"}]}]},{"version":"2.x","default":false,"pages":[{"title":"2.x","href":"/get-started/introduction-to-authlete/overview"}]}]},{"language":"ja","pages":[{"title":"ja","href":"/ja/configuration-reference/endpoints/handling-request-parameters"}]}]},"title":"Handling Parameters in Authorization Requests and Token Requests - Authlete Documentation","buildId":"dpl_849ArpqvBiCczQiT1Y1stNGpbqHT","deploymentId":"dpl_849ArpqvBiCczQiT1Y1stNGpbqHT","dynamics":["a74be98ba7"],"chunks":["zoom-image-lightbox-CaUwvYH3.js","lightbox-handle-r17bVUz3.js"]}